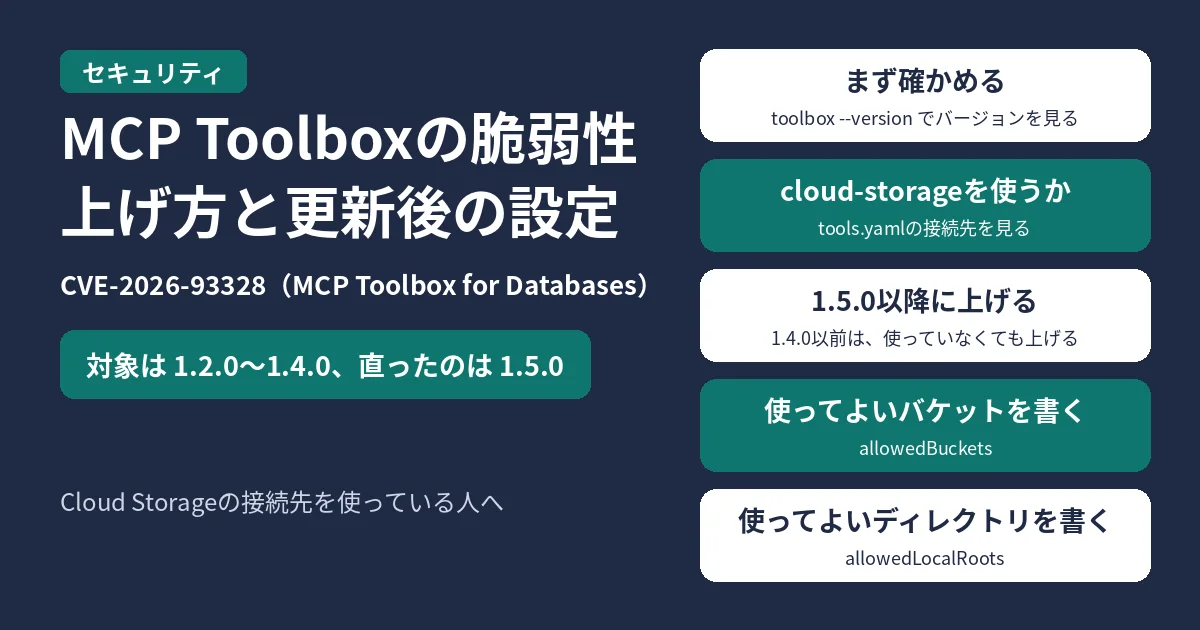
Google Cloudの
cloud-storageをallowedBuckets と allowedLocalRoots を
toolbox --versionnpxや
表示された
- 2026年10月27日7時57分
(日本時間) 時点の、 CVEの 記録・ NVD・ GitHubの リリースノートと 公式ドキュメントの 内容です。 - 深刻度は
CVSS 4.0で 9.3 (Critical)です。 CVEを 登録した Google Cloudが 付けた 値です。 - 認証なしで
外から、 Toolboxを 動かしている マシンの ファイルを 外部の Cloud Storageの バケットへ 持ち出されたり、 ローカルの ファイルを 上書きされたりする おそれが あります。
結論:当てはまるかと、やること
| 使い方 | やること |
|---|---|
| 1.2.0〜1.4.0で |
1.5.0以降にallowedBuckets・allowedLocalRoots を |
| 1.5.0以降で |
allowedBuckets・allowedLocalRoots が |
| 1.4.0以前で |
この |
| 1.5.0以降で |
この |
cloud-storageの
CVE-2026-93328とは
MCP Toolbox for Databasesは、
CVE-2026-93328は、type: cloud-storage)で、cloud-storage-upload-object と cloud-storage-download-object です。
| 項目 | 内容 |
|---|---|
| CVE | CVE-2026-93328 |
| 深刻度 | CVSS 4.0で |
| 種類 | パストラバーサル |
| 影響する |
1.2.0〜1.4.0 |
| 直った |
1.5.0 |
| 悪用の状況 | NVDに |
| GitHub | アドバイザリの |
公開の
| 日時 | できごと |
|---|---|
| 5月8日 4時18分 | 1.2.0が |
| 6月18日 10時38分 | 修正の |
| 6月19日 8時34分 | 1.5.0が公開 |
| 10月23日 9時14分 | 1.15.0が公開 |
| 10月26日 23時24分 | CVE-2026-93328が公開 |
| 10月27日 0時16分 | NVDに載る |
| 10月27日 0時34分 | GitHubの |
自分のバージョンを確かめる
バイナリで動かしているとき
toolbox --versionWindowsでは
.\toolbox.exe --version次のように
toolbox version 1.15.0+binary.linux.amd64.8e8e569npxで動かしているとき
npx @toolbox-sdk/server --versionコンテナで動かしているとき
docker ps --format "{{.Image}}"イメージ名の
cloud-storageを使っているか
設定ファイルtype: cloud-storage の--prebuilt cloud-storage が
grep -n "cloud-storage" tools.yaml1.5.0以降に上げる
1.5.0では、mcpEnabled をaudience か clientId がenable-api を
バイナリ(Linux・AMD64の例)
export VERSION=1.15.0
curl -L -o toolbox https://storage.googleapis.com/mcp-toolbox-for-databases/v$VERSION/linux/amd64/toolbox
chmod +x toolbox
sha256sum toolbox
表示された
Homebrew
brew upgrade mcp-toolboxコンテナ
docker pull us-central1-docker.pkg.dev/database-toolbox/toolbox/toolbox:1.15.0今の
npx
npx @toolbox-sdk/server@1.15.0 --config tools.yamlGoで入れているとき
go install github.com/googleapis/mcp-toolbox@v1.15.0上げた
上げたあとに入れる設定
1.5.0で、
| 設定 | 決めること |
|---|---|
allowedBuckets |
使って |
allowedLocalRoots |
ファイルの |
公式ドキュメントの
kind: source
name: my-gcs-source
type: "cloud-storage"
project: "my-project-id"
allowedBuckets:
  - "my-app-bucket"
  - "my-backup-bucket"
allowedLocalRoots:
- "/workspace"- 1.10.0以降は、
Toolboxが シンボリックリンクを たどった 先も、 許可した ディレクトリの 中に あるかを 確かめます。 ハードリンクは 区別できません。 --prebuilt cloud-storageの公式の 設定には、 allowedBuckets・allowedLocalRootsが書かれていません。 2つを 設定する ときは、 tools.yamlに 接続先を 書きます。 - Google Cloudは
CVEの 記録で、 あわせて Toolboxを 権限の 少ない OSの ユーザーで 動かし、 IAMの 権限を しぼるよう 勧めています。
1.5.0に入ったほかのセキュリティ修正
1.5.0の
- HTTPの
接続先と Cloud Healthcareの 接続先で、 SSRF(サーバーに 意図しない 宛先へ 通信させる 攻撃)を 防ぐ チェックを追加 bigquery-execute-sqlで、データセットの 制限を すり抜けられる 問題を修正 mysql-get-query-planで、クエリの 実行や 別の 文の 差し込みが できる 問題を修正 - SQLインジェクションを
防ぐ ため、 区切り文字の エスケープを修正 - MCPの
HTTPで 受け取る データの 大きさに 上限を設定

コメント